Hi
During tests performed by one of my customers we discovered that ClearPass sends a retry to Entra ID in case the service isn't available. Is this an expected behavior?
In the Source configuration there are no options to configure the number of retries.
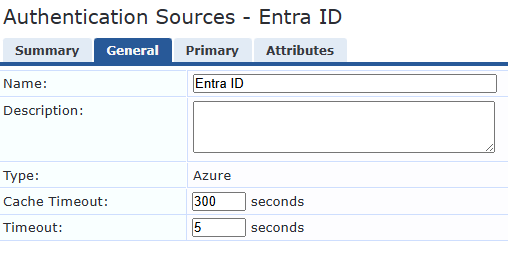
In this specific environment the the RADIUS server configuration was configured with a 5 second timeout. So if Entra ID wasn't accessible ClearPass needed 2x5 seconds to respond with the correct enforcement profile. But at that time the WLAN infrastructure had already considered it as a RADIUS server timeout.
By default this Entra ID timeout is 60 seconds, and with a retry it will reach 120 seconds. No RADIUS authentication in the world will be that patient... 😅
We have now changed the Entra ID timeout to just 1 second and tests show that normal Entra ID response time is about 200 ms.
| 2026-08-27 13:16:38,091 |
[Th 7802 Req 26753221 SessId R000cba62-04-6a901c95] INFO RadiusServer.Radius - rlm_eap_tls: Session established. |
| 2026-08-27 13:16:38,091 |
[Th 7802 Req 26753221 SessId R000cba62-04-6a901c95] INFO RadiusServer.Radius - rlm_eap_tls: Initiating policy evaluation |
| 2026-08-27 13:16:38,091 |
[Th 7802 Req 26753221 SessId R000cba62-04-6a901c95] INFO RadiusServer.Radius - rlm_policy: Starting Policy Evaluation. |
| 2026-08-27 13:16:39,100 |
[HttpModule-ThreadPool-3-0x7fbc08544700 r=R000cba62-04-6a901c95 h=129] ERROR Http.HttpAutzSession - execute: get::<easy_perform>, (error=28) Timeout was reached |
| 2026-08-27 13:16:39,100 |
[HttpModule-ThreadPool-3-0x7fbc08544700 r=R000cba62-04-6a901c95 h=129] ERROR BaseExtSvr.ExtSvrSession - Unable to get next handle from manager with name=Customer-Entra |
| 2026-08-27 13:16:39,100 |
[RequestHandler-1-0x7fbbb85e2700 h=21321533 c=R000cba62-04-6a901c95] INFO Core.PETaskRoleMapping - Roles: Customer-IT, Customer-Staff, Customer-Staff_all, Customer-site_Campus, Machine Authenticated] |
| 2026-08-27 13:16:39,100 |
[RequestHandler-1-0x7fbbb85e2700 r=R000cba62-04-6a901c95 h=21321531 c=R000cba62-04-6a901c95] INFO Core.PETaskScheduler - ** Completed PETaskRoleMapping ** |
| 2026-08-27 13:16:39,100 |
[RequestHandler-1-0x7fbbb85e2700 r=R000cba62-04-6a901c95 h=21321531 c=R000cba62-04-6a901c95] INFO Core.PETaskScheduler - ** Starting PETaskPolicyResult ** |
| 2026-08-27 13:16:39,100 |
[RequestHandler-1-0x7fbbb85e2700 r=R000cba62-04-6a901c95 h=21321531 c=R000cba62-04-6a901c95] INFO Core.PETaskScheduler - ** Completed PETaskPolicyResult ** |
| 2026-08-27 13:16:39,100 |
[RequestHandler-1-0x7fbbb85e2700 r=R000cba62-04-6a901c95 h=21321531 c=R000cba62-04-6a901c95] INFO Core.PETaskScheduler - ** Starting PETaskEnforcement ** |
| 2026-08-27 13:16:40,000 |
[HttpModule-ThreadPool-14-0x7fbbcedf6700 r=R000cba62-04-6a901c95 h=140] ERROR Http.HttpAutzSession - execute: get::<easy_perform>, (error=28) Timeout was reached |
| 2026-08-27 13:16:40,000 |
[HttpModule-ThreadPool-14-0x7fbbcedf6700 r=R000cba62-04-6a901c95 h=140] ERROR BaseExtSvr.ExtSvrSession - Unable to get next handle from manager with name=Customer-Entra |
| 2026-08-27 13:16:40,000 |
[RequestHandler-1-0x7fbbb85e2700 h=21321558 c=R000cba62-04-6a901c95] INFO Core.PETaskEnforcement - EnfProfiles: Customer-IT, Customer-Staff-vlan-Campus |
| 2026-08-27 13:16:40,000 |
[RequestHandler-1-0x7fbbb85e2700 r=R000cba62-04-6a901c95 h=21321531 c=R000cba62-04-6a901c95] INFO Core.PETaskScheduler - ** Completed PETaskEnforcement ** |
| 2026-08-27 13:16:40,000 |
[RequestHandler-1-0x7fbbb85e2700 r=R000cba62-04-6a901c95 h=21321531 c=R000cba62-04-6a901c95] INFO Core.PETaskScheduler - ** Starting PETaskRadiusEnfProfileBuilder ** |
------------------------------
Best Regards
Jonas Hammarbäck
MVP Guru, ACEX, ACDX #1600, ACCX #1335, ACX-Network Security
Aranya AB
If you find my answer useful, consider giving kudos and/or mark as solution
------------------------------